Cave de Genève
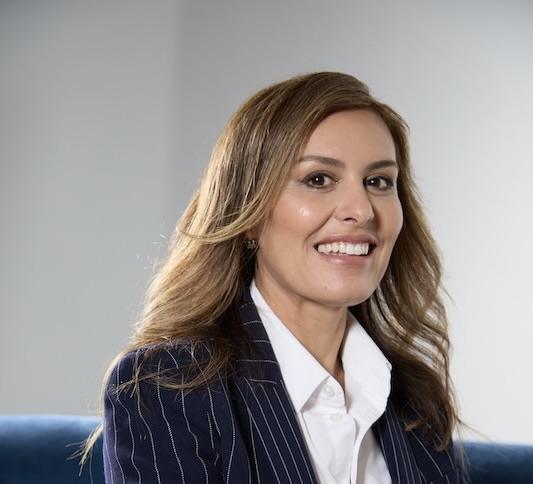
Roger Imboden, CEO of Imboden Global Trading & Consulting, speaks about the Industrial Revolution 4.0 and the major risks of the 21st century.
“An indispensable requirement of risk management”
 Le Monde Economique: Seen as the point of convergence between the virtual world of digital technologies and the production of real-world objects, Industry 4.0 aims to create smart factories capable of optimizing their resources and production capacity. What are the challenges of this fourth industrial revolution?
Roger Imboden : A smart factory is made up of cyber-physical systems that connect the real and virtual worlds. It is characterized primarily by automation of the production chain and by the connectivity of software, equipment, workforce and data. This is a radical shift that brings many challenges. As human capital becomes interconnected with high-tech infrastructure, new skills are required. A company — particularly human resources — must identify the cognitive skills of employees and implement them in the smart production process in order to combine natural and artificial intelligence as effectively as possible. The new systems and infrastructures collect and process large volumes of data. Companies are increasingly faced with the challenge of securing IT infrastructure and protecting data, in order to avoid business interruption scenarios, theft and breaches of data confidentiality, damage to reputation, and so on. In the context of factory digitalization, all employees, including the board of directors and the executive committee, are concerned by these challenges, not just the IT department.
Le Monde Economique: Studies carried out in Germany and the United States have shown that, among the vast majority of industrial workers, the skills required for Industry 4.0 are not in place. Is Switzerland facing the same reality?
Roger Imboden : A range of indicators suggests that Switzerland is not ready today to meet the skills challenge. Requirements will become increasingly technical, not only in the long term, but also in the short term. The reason is that industrial companies are already facing a shortage of highly qualified digital talent. In addition, several reports confirm that a significant proportion of jobs is exposed to technological change. This is a key issue as companies move toward Industry 4.0. If Swiss industry is to maintain a competitive edge in the market through innovation, it must not seek to hire the required skills abroad or relocate smart factories; both of these aspects are crucial. The retraining of employees through the implementation of a specific concept is effective. In this context, we speak of “HR 4.0”. In addition, several reports confirm that pupils in primary school, lower secondary school and gymnasium are insufficiently prepared for digital transformation. It is important to question part of the education system and to integrate technical modules into the curriculum that are essential for Industry 4.0.
Le Monde Economique: When technologies were connected on an internal network and centralized in the same building, securing everything was easier. Does the multiplication of data and systems within the company not highlight the importance of cybersecurity?
Roger Imboden : With the arrival of digital transformation, and especially Industry 4.0 factories, everything is interconnected. We can see that many companies focus on the functional aspect of the smart factory’s production capabilities. Security aspects are often neglected, with heavy consequences. Cyberattacks against smart factories are increasing. The exchange points between tools and production lines are all connected to the world at large. Business interruption, theft of projects and data, blackmail, to name just three examples. To minimize the risks of such an incident, it is essential to invest in IT security.
Le Monde Economique: In this new configuration, can you explain the risks and vulnerabilities?
 Roger Imboden : The new setup, with all its innovations, brings with it several sources of risk and vulnerability. Hyper-connectivity and exchanges between production systems are intensifying. The entry points for attacks are numerous. Attacks rely on the psychology of human beings as much as on IT infrastructure. Every employee can be a weak point. Clicking on an infected PDF file carrying a Trojan horse that contains malware can allow attackers to steal sensitive data, take control of production, or block it. The same applies to a company’s IT infrastructure or that of a smart factory.
Le Monde Economique: As of May 2018, the new EU regulations will require companies to step up their cybersecurity practices. Will this be an opportunity or a risk?
Roger Imboden : A company is not affected by the GDPR if it provides services only in Switzerland and does not process any personal data belonging to EU citizens. The introduction of the GDPR is a cultural shift, because it imposes many new requirements linked to the implementation of new operational processes and a “top down” approach. From a corporate perspective, the new legislation is therefore often seen at first glance as a risk. But if we look further ahead, we can see that it can also be considered an opportunity from a governance standpoint, as it enables better security. For today’s clients, security is a criterion when choosing a service. We are in the midst of companies’ digital transformation. Hence the importance of strengthening the balance between security and data confidentiality. The change in practices within companies will be fundamental. Implementing the new measures will improve security through a well-secured infrastructure that is regularly reviewed with controls and a strict design, as well as analyses and the development of an action plan to deal with incidents. This is a positive step and an opportunity for all parties involved.
Le Monde Economique: A new study by Palo Alto Networks shows that there is still much to be done in terms of preventing cyber breaches. What recommendations do you have to strengthen an IT environment?
Roger Imboden : Zero risk does not exist. We recommend and implement for our clients a global cyber-governance approach with risk management, which links prevention and risk transfer, and which will make it possible to recover quickly in the event of a fall, with limited damage. A cyber audit with penetration testing and social engineering can identify risks and vulnerabilities. This report also helps reduce such risks. It is also necessary to put in place a cybersecurity policy and strategy, with business continuity and crisis-management plans. Staff must be trained continuously and must be able to rely on an IT charter. Permanent monitoring is essential. The remaining risk can be transferred to an insurance company. In the United States, for example, almost every company has had a cyber plan and cyber insurance for several years. A company unprepared for this risks bankruptcy, as history has shown us. The recommendation is prevention, risk analysis and post-loss support.